Warum wir bei Evoex Sicherheit anders betrachten
Als wir bei Evoex unsere Infrastruktur planten, haben wir uns für einen anderen Weg entschieden. Nicht abwarten und reagieren, sondern versuchen, das Auftreten von Problemen von vornherein zu verhindern.
In this year's Midsummer break, something unforgettable happened in Latvia's IT sector — an attack on Latvia's State Forest IT infrastructure. The attack was discovered on June 22, 2026, but it later emerged that the hacker had penetrated the system already on June 11th and operated undetected for several days, only beginning active operations during the night of June 22-23.
It reminded everyone working in this field of one simple, yet uncomfortable truth: if security is only addressed after something has already happened, it's already too late. Configuration gaps and undiscovered vulnerabilities in a system can remain hidden for a long time until someone finds them — and unfortunately, that someone is often not the person it should be.
When we at EvoEX planned our infrastructure, we chose the opposite approach. Not to wait and react, but to try to prevent problems from arising in the first place.
1. Security begins before code reaches the server
In our development process, no change reaches the production server without undergoing complete automated verification. Every new piece of code is analyzed in real time by specialized security tools based on globally recognized OWASP Top 10 principles — this is the standard used to identify the most common and dangerous types of vulnerabilities.
If the tools detect even the smallest risk, the change is not released further. The system itself attempts to fix the problematic code section, re-checks it, and the process continues, until the risk count is exactly zero. Only then can changes reach users.
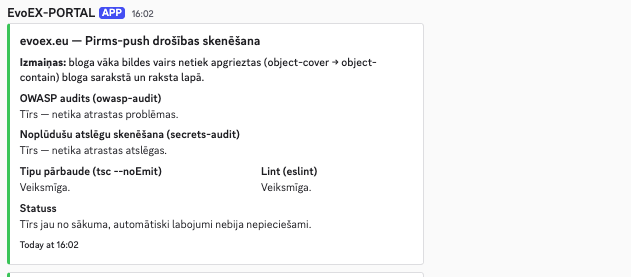
Our team receives this notification every time changes pass through the complete security audit and auto-remediation cycle before deployment.
2. Servers that have nothing to lose from the outside
One of the simplest, yet frequently overlooked security principles — if doors are not open, they cannot be broken through. Our servers run on Hetzner infrastructure, and we have completely closed the external connection ports traditionally used for remote server access. Instead, the server itself, from within, monitors an authorized code repository and, when everything has been verified and is secure, pulls in the updates. No one can "knock" from outside because there are simply no doors there.
Additionally, websites have strict security headers implemented (HSTS, X-Content-Type-Options, X-Frame-Options, Referrer-Policy), which protect users from data interception, website cloning, and other common attack types.
3. When someone tries anyway
It is impossible to completely prevent attack attempts — the internet is full of automated bots that constantly scan websites and look for weak spots. That's why we built our own system that detects these attempts and responds immediately.
If, for example, a brute-force attempt or suspicious scanning is detected, the attacker's IP address is immediately blocked at the firewall level. But the work doesn't stop there — our custom analysis tool immediately begins investigating what happened: what were the requests, what was their pattern, what was the attacker trying to achieve. The result is a brief, clear report in Latvian that is instantly delivered to our engineering team's Discord channel. This way we not only stop the attempt but also know exactly what happened.
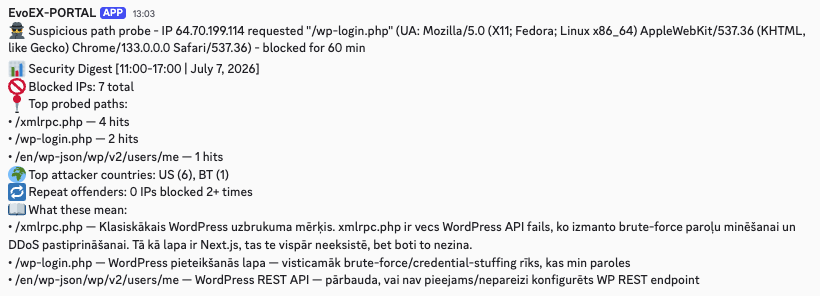
A real example from our system — a suspicious request is blocked immediately, and every hour an automated summary of all attempts, their origins, and probable intent is generated.
4. What this means for the client
Wenn Sie sich für EvoEX entscheiden, erhält der Klient nicht nur eine Website oder ein System – er erhält eine Infrastruktur, in der Sicherheit keine Nachgedanke ist, sondern das Fundament.
Fehler werden erkannt und behoben, bevor sie das Internet erreichen, nicht danach, wenn bereits etwas passiert ist.
Angriffsmöglichkeiten werden auf ein Minimum reduziert – es gibt einfach keine Türen zum Anklopfen.
Das System arbeitet und lernt kontinuierlich, nicht nur einmal im Jahr, wenn jemand sich daran erinnert, eine Sicherheitsprüfung in Auftrag zu geben.
Alle Updates erfolgen im Hintergrund, sodass Websites und Portale ohne Unterbrechung weiterarbeiten.
Cybersicherheit ist kein Prozess, den man "einmal repariert und vergisst". Es ist eine ständige Arbeit. Und wir denken – je weniger unsere Kunden sich darüber Sorgen machen müssen, desto besser machen wir unsere Arbeit.
5. Warum wir davon sprechen
Wir haben all das nicht aufgebaut, weil jemand von uns es verlangt hat. Im letzten Jahr haben wir mehrere tausend Euro investiert, um dieses System aufzubauen und weiterhin zu entwickeln – Zeit, Werkzeuge und selbst entwickelte Software, die heute im Hintergrund läuft, ohne Unterbrechung, jeden Tag.
Dies ist keine einmalige Investition, die man abhaken und vergessen kann – es ist eine Infrastruktur, in die wir weiterhin investieren, weil wir wissen, dass sich die Methoden der Angreifer schneller ändern, als die meisten Unternehmen reagieren können.
Der LVM-Fall zeigte, dass selbst große Unternehmen mit Ressourcen genau das brauchen können – ein System, das das Problem selbst erkennt, bevor es zur Krise wird.
Wir haben nicht gewartet, bis so etwas bei uns oder unseren Kunden passiert. Wir haben Zeit und Geld investiert, um eine Infrastruktur aufzubauen, die von Grund auf robust ist, nicht nur, wenn jemand nach einem Vorfall Schuldige sucht.
Das bedeutet, dass ein Klient, der sich für EvoEX entscheidet, sich nicht Sorgen machen muss, ob seine Daten und sein System nach dem Restprinzip geschützt sind. Sicherheit ist kein zusätzlicher Service, den man später hinzufügen kann – sie ist bereits in jedem Projekt eingebaut, das wir entwickeln.
Wenn du interessiert bist, wie die Sicherheit deiner Website oder deines Systems von außen aussieht, kontaktiere uns – wir evaluieren das zusammen und sagen dir ehrlich, wo die Risiken sind und was man dagegen tun kann.
Buche dein Audit – EvoEX Audit ab 390 EURO
Passende Leistungen
Bereit, dein Projekt zu starten?
Erzähl uns von deiner Idee — wir schicken dir per E-Mail einen vorgeschlagenen Termin für ein Videogespräch, um die Details zu besprechen und ein Angebot zu erstellen.