Kui me Evoexis oma infrastruktuuri planeerisime, valisime vastupidise lähenemisviisi. Me ei otsustanud oodata ja reageerida, vaid püüdsime probleemide tekkimist üldse ära hoida.
This past Midsummer break, Latvia's IT sector witnessed something unforgettable - an attack on Latvia's State Forests IT infrastructure. The attack was discovered on June 22, 2026, but it later emerged that the hacker had already gained access to the system on June 11 and had operated undetected for several days, only beginning active operations during the night of June 22–23.
It reminded everyone working in this field of one simple, yet uncomfortable truth: if security is only addressed after something has already happened, it's already too late. Configuration gaps and undiscovered vulnerabilities can remain hidden in a system for long periods, until someone finds them - and unfortunately, it's often not the person who should.
When we at Evoex planned our infrastructure, we chose a different path. Not to wait and react, but to try to prevent problems from arising in the first place.
1. Security starts before code reaches the server
In our development process, no change reaches the production server without a complete automated check. Every new piece of code is analyzed in real-time by specialized security tools based on globally recognized OWASP Top 10 principles - the standard used to identify the most common and dangerous types of vulnerabilities.
If the tools detect even a minor risk, the change is not released. The system itself attempts to fix the problematic code section, checks it again, and the process continues until the number of risks is precisely zero. Only then can changes reach users.
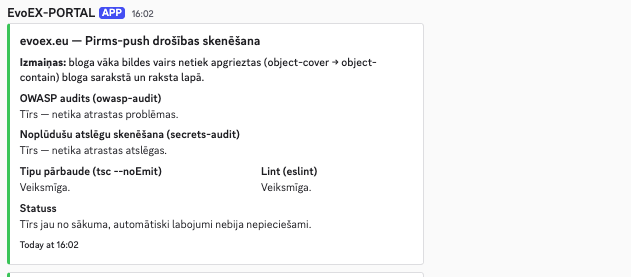
Our team receives such a notification every time changes pass through the complete security audit and auto-repair cycle before deployment.
2. Servers with nothing to lose from the outside
One of the simplest, yet often forgotten security principles - if doors aren't open, they can't be broken into. Our servers operate on Hetzner infrastructure, and we have completely closed the external connection ports traditionally used for remote server access. Instead, the server itself, from the inside, checks an authorized code repository and, when everything has been verified and is secure, pulls updates. No one can "knock" from outside, because the doors simply don't exist there.
In addition, the websites have strict security headers in place (HSTS, X-Content-Type-Options, X-Frame-Options, Referrer-Policy) that protect users from data interception, site cloning, and other common types of attacks.
3. When someone tries anyway
It's impossible to completely eliminate attack attempts - the internet is full of automated bots that constantly scan websites and search for weak spots. That's why we created a system that detects these attempts and responds immediately.
If, for example, a brute-force attempt or suspicious scanning is detected, the attacker's IP address is blocked immediately at the firewall level. But the work doesn't stop there - our custom analysis tool immediately begins investigating what happened: what were the requests, what was their pattern, what was the attacker trying to achieve. The result is a brief, understandable report in Estonian that immediately reaches our engineering team's Discord channel. This way we not only stop the attempt, but also know exactly what happened.
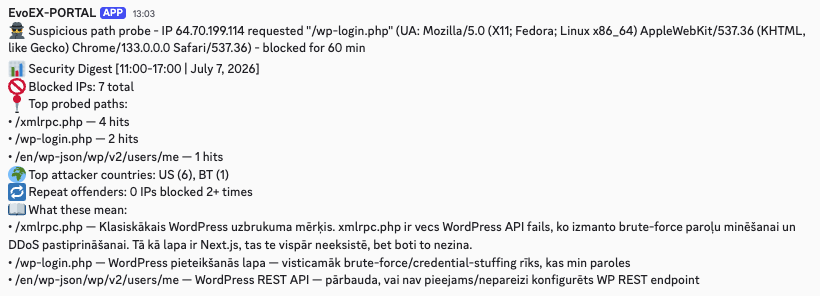
A real example from our system - a suspicious request is blocked immediately, and every hour an automated summary of all attempts, their origins, and possible intentions is generated.
4. What this means for the client
Valides Evoex-i, ei saa klient mitte lihtsalt veebilehte või süsteemi - ta saab infrastruktuuri, kus turvalisus pole tagantjärgi, vaid alus.
Vead leitakse ja parandatakse enne internetisse jõudmist, mitte pärast seda, kui midagi on juba juhtunud.
Rünnakute võimalused on viidud miinimumini - lihtsalt pole uksi, millele koputada.
Süsteem töötab ja õpib pidevalt, mitte ainult kord aastas, kui keegi mäletab tellimusjärjekorras turvalisuse auditi.
Kõik uuendused toimuvad taustal, nii et veebisaidid ja portaalid töötavad jätkuvalt ilma katkestusteta.
Küberturvalisus pole protsess, mida saab "korraga korda seada ja unustada". See on pidev töö. Ja meie arvates - mida vähem peavad meie kliendid selle pärast muretsema, seda paremini me seda teeme.
5. Miks me sellest räägime
Me ei loonud seda kõike sellepärast, et keegi meilt seda nõudis. Viimase aasta jooksul oleme investeerinud tuhandeid eurosid selle süsteemi ehitamiseks ja arendamiseks - aega, vahendeid ja enda loodud tarkvara, mis täna töötab taustal, ilma katkestusteta, iga päev.
See pole korraga tehtav investeering, mida saab märkida ja unustada - see on infrastruktuur, kuhu jätkame investeerimist, sest teame, et rünnakute meetodid muutuvad kiiremini kui enamus ettevõtteid reageerida suudab.
LVM juhtum näitas, et isegi suurtel ettevõtetel ressurssidega võib puududa just see - süsteem, mis ise märkab probleemi enne kui see saab kriisiks.
Me ei ootanud, kuni midagi sellist juhtub meile või meie klientidele. Oleme investeerinud aega ja raha infrastruktuuri ehitamiseks, mis on juba alusest alates vastupidav, mitte ainult siis, kui keegi intsidendi järel hakatakse süüdlast otsima.
See tähendab, et klient, kes valib Evoex-i, ei pea muretsema, kas tema andmed ja süsteem on kaitstud jääkkaaluse järgi. Turvalisus pole lisateenuse, mida saab hiljem lisada - see on juba iebūveerd igasse projekti, mida me loome.
Kui teid huvitab, kuidas näeb teie veebisait või süsteem välja väljastpoolt turvalisuse seisukohast, võtke meiega ühendust - hindame seda koos ja ütleme ausalt, kus on riskid ja mida nendega teha.
Registreerige oma audit - Evoex Audit alates 390 EURO
Seotud teenused
Valmis oma projekti alustama?
Räägi meile oma ideest — saadame sulle e-kirjaga pakutud aja videokõneks, kus arutame detaile ja koostame pakkumise.